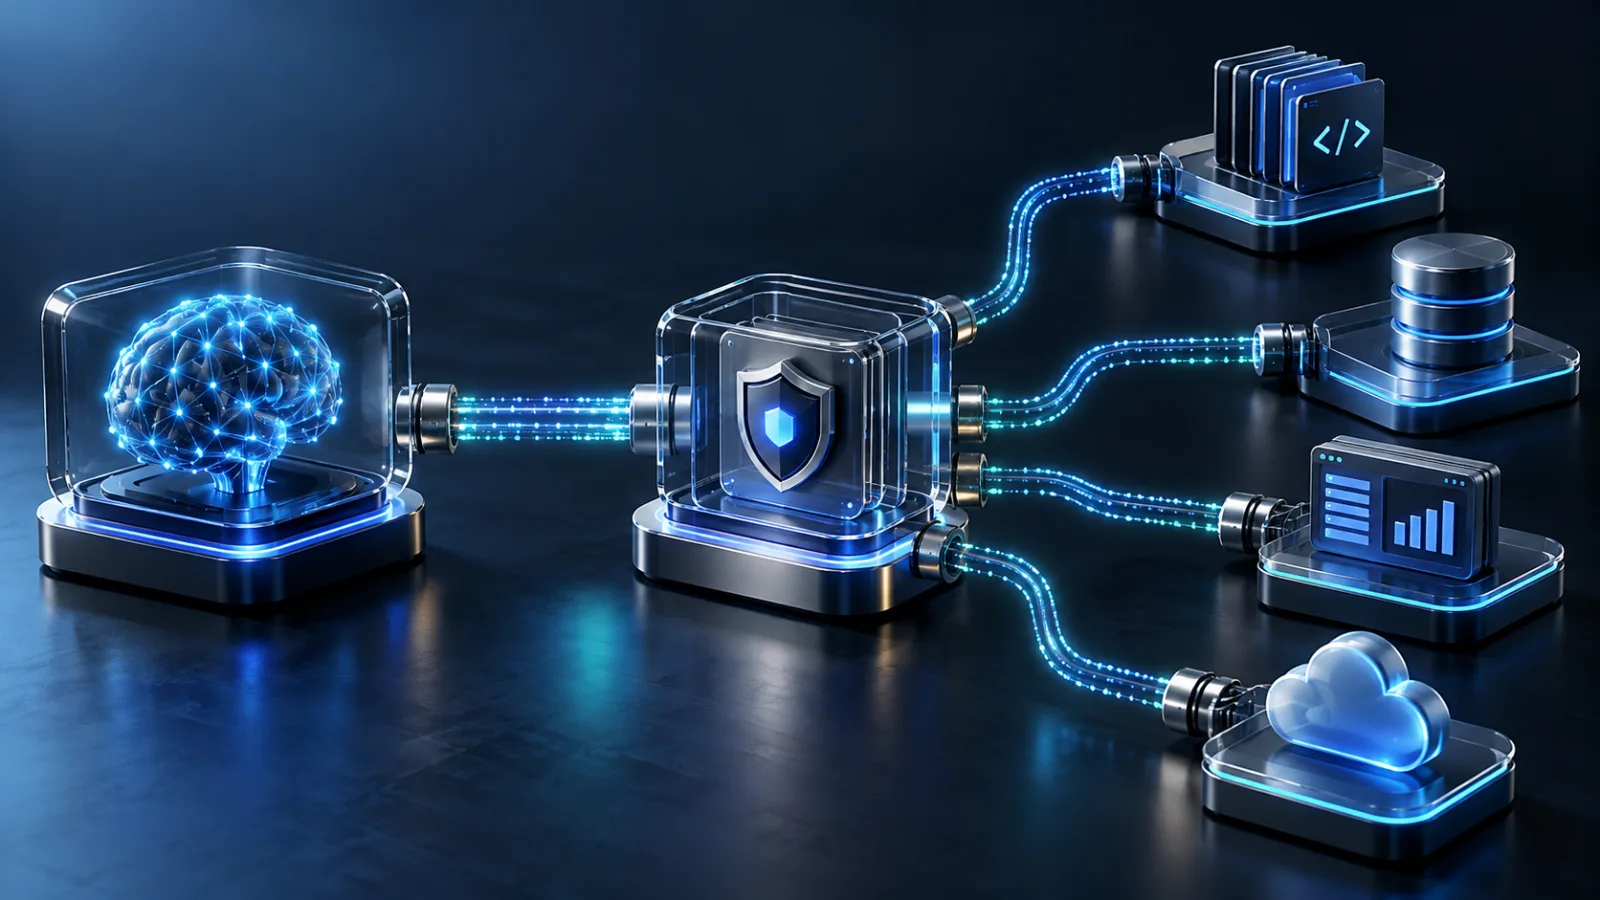
A language model can write a convincing answer about a customer record without ever seeing that record. It can describe how to open a support ticket without having permission to create one. That gap between fluent reasoning and controlled access to real systems is where Model Context Protocol becomes useful.
I think of MCP as a contract at the edge of an AI application. The host can ask what a server offers, inspect the input schema, call a narrowly defined tool, read a resource, and handle a structured result. The server can protect the system behind it without knowing which model or chat interface initiated the request.
This matters once an experiment grows beyond a couple of hard-coded functions. A serious assistant may need a repository, a document store, a ticketing platform, and an internal API. Building each connection differently creates avoidable work and, more concerningly, inconsistent security. MCP gives those connections a common shape.
A technical definition of MCP
Model Context Protocol is an application-layer protocol, based on JSON-RPC 2.0, for exchanging context and capability calls between an AI host and external MCP servers. It defines message shapes, lifecycle behavior, capability discovery, and standard operations. It does not define the model, agent loop, database, or business API behind the connection.
- Messages: requests expect a response, responses contain a result or error, and notifications report events without requiring a response.
- Transports: local integrations commonly use standard input/output, while remote MCP servers use Streamable HTTP. Transport carries the protocol messages but does not change their meaning.
- Capabilities: client and server advertise what they support. A host should use only the operations available for the negotiated protocol revision and connection.
- Server primitives: tools expose callable actions, resources expose addressable context, and prompts expose reusable interaction templates.
- Control boundary: the host controls model context, user interaction, and consent; the server validates requests and protects the underlying system.
Why MCP exists
Without a shared protocol, every AI application grows its own collection of adapters. Add another assistant or model provider and the same integrations are built again. Soon, a small backend change breaks several clients in slightly different ways. I have seen this pattern before with point-to-point enterprise integrations; AI does not make the maintenance problem disappear.
Custom tool calling works for a prototype. It becomes expensive when the number of models, AI agents, applications, and business systems grows. Governance also fragments because each connector invents its own schema, permissions, errors, and prompt conventions.
MCP standardizes how an AI application discovers and uses external capabilities. The underlying API, database, vector store, or SaaS platform still does the real work. An MCP server adds a protocol-facing layer so an AI host can discover what is available, understand typed inputs, call the right capability, and receive a structured result.
MCP is valuable because it makes the connection predictable. The model may change; the contract around tools, context, and permission can remain understandable.
From Anthropic to an open AI ecosystem
Anthropic introduced and open-sourced Model Context Protocol in November 2024. The original idea was direct: replace fragmented, one-off AI integrations with an open standard for secure connections between AI assistants and the systems where data and tools live. Claude Desktop and Claude Code helped many developers encounter MCP for the first time, establishing Anthropic MCP servers as an early reference point for the ecosystem.
The protocol quickly expanded beyond one company or model. In December 2025, Anthropic donated MCP to the Agentic AI Foundation under the Linux Foundation. The foundation brought together Anthropic, Block, and OpenAI alongside other major technology companies to support neutral, community-led infrastructure for agentic AI.
OpenAI describes itself as an early MCP adopter and core contributor, using the protocol as a foundation for connectors and apps in ChatGPT. For developers, the OpenAI Agents SDK includes MCP server integration for hosted remote servers, Streamable HTTP, and local stdio connections. That means an OpenAI agent can discover and call MCP tools alongside its other capabilities.
Anthropic and OpenAI approach agent products differently, but their support for MCP points to the same architectural idea: tools and context become more valuable when they are portable across AI applications. MCP is therefore best understood as model-neutral infrastructure. An MCP server can serve Claude, ChatGPT, an OpenAI API agent, a coding assistant, or a custom LLM application when the host supports the protocol.
A useful mental model: host, client, server
The architecture separates three responsibilities. Following a request through these roles is the clearest way to understand the protocol:
- The MCP host is the AI application a person uses. It owns the conversation, orchestrates the AI agent, assembles context, and remains responsible for consent and policy.
- The MCP client lives inside the host. It manages a protocol connection and exchanges structured messages with one MCP server.
- The MCP server exposes focused capabilities backed by real services or data. It might wrap a knowledge base, source-control platform, CRM, ticketing system, browser automation service, or internal API.
MCP architecture at a glance
Select a layer to see its responsibility.
The MCP server does not need to know how the final chat, copilot, or autonomous agent experience is designed. The host does not need a one-off connector for every underlying system. Both sides can evolve around the same protocol contract.
Tools, resources, and prompts
At the capability boundary, an MCP server exposes three core primitives. Each gives the AI application a different kind of access and assigns control differently.
Three primitives, three kinds of context
Explore what an MCP server can expose.
MCP tools perform actions or computations. A tool can accept typed parameters, call a backend, and return a structured result. MCP resources provide addressable context such as documents, code, schemas, or records. MCP prompts are reusable interaction templates that a person can select to begin a known workflow.
The distinction is more than terminology. It prevents teams from treating every piece of context as another block of prompt text. A document can remain an addressable resource. A repeated workflow can be a prompt. A consequential operation can be a typed tool with an approval boundary. That separation makes the system easier to reason about and audit.
How an MCP request flows
A reliable MCP interaction is a sequence of bounded protocol and application decisions. The exact lifecycle varies by protocol revision and transport, but the operational process remains consistent.
From intent to a governed action
A reliable integration makes every boundary visible.
- Connect and negotiate: the client opens a supported transport and establishes the protocol revision and capabilities used by the connection.
- Discover: the client obtains available tools, resources, or prompts through list operations such as
tools/list. - Select: the host presents relevant schemas to the model. The model proposes the capability and arguments that match the user’s intent.
- Authorize: the host evaluates identity, scopes, organizational policy, and user consent before a sensitive operation.
- Execute: the client sends an operation such as
tools/call,resources/read, orprompts/get. The server validates the request before touching the underlying system. - Return: the server responds with typed content, structured data, metadata, or a protocol error. The host decides what enters the model context.
- Continue and observe: the agent loop interprets the result, produces an answer or another bounded action, and records traces and audit events.
Tool descriptions deserve the same care as a public API. A vague operation such as update_record tells the model and the user almost nothing. I would rather expose a narrow operation with explicit inputs, a clear consequence, and a bounded result. It is easier to approve, test, observe, and remove later.
One MCP transaction, told as a technical story
Start with the user intent: “Find the current incident affecting service A and prepare a follow-up task.” The host sends the intent and the available tool definitions to the model. The model does not call the backend directly; it produces a structured proposal to use search_incidents with a service identifier.
The host checks whether that tool is permitted and whether approval is required. The MCP client then serializes the call and sends it to the incident server. The server validates the JSON arguments, applies its own authorization rules, calls the incident API, and maps the response into MCP content blocks.
The host adds the structured result to the model context. The model can now summarize the incident and propose create_follow_up_task on a different MCP server. Because that operation changes external state, the host pauses for explicit approval. After approval, the second server executes the action and returns the new task identifier. The host presents the final result and preserves the trace.
That sequence is the technical narrative of MCP: intent becomes a typed capability request; policy gates the side effect; the server owns backend validation; and the result returns as structured context for the next model turn.
Design the boundary around the job
An MCP server should expose the smallest coherent capability needed for the workflow. Do not mirror an entire internal API merely because it already exists. Start from the user’s job, publish narrow operations, and keep business validation in the system that owns the data.
Keep deterministic controls outside the model
The LLM can interpret intent, choose among permitted tools, and summarize results. Authentication, authorization, validation, rate limits, transaction limits, and audit logging belong in deterministic application and MCP server code.
An adoption checklist for engineering leaders
- Choose one measurable AI workflow. Select a repeated task with clear users, system owners, and an outcome you can evaluate.
- Inventory existing APIs and data sources. MCP usually wraps capabilities you already trust; it should not duplicate core business logic.
- Define agent control explicitly. Decide which context the application supplies, which tool calls the model may propose, and where a person must approve.
- Threat-model the whole path. Include prompt injection, tool poisoning, confused-deputy risks, excessive scopes, data leakage, replay, and unsafe side effects.
- Make MCP tools narrow and typed. Use descriptive names, strict JSON schemas, bounded outputs, and actionable error responses.
- Evaluate agent behavior, not just connectivity. Test tool selection, argument quality, refusal behavior, latency, failure recovery, and user comprehension.
- Instrument from day one. Track MCP calls, approvals, errors, latency, token use, and business outcomes without collecting unnecessary data.
What MCP does not solve
MCP does not choose the right product experience, fix a weak authorization model, guarantee trustworthy data, or eliminate AI evaluation. It is an interoperability standard. Architecture quality still depends on the boundaries around it.
It also does not replace APIs, retrieval-augmented generation, or an agent framework. An MCP server often adapts existing APIs into capabilities suited to AI applications. RAG can retrieve relevant knowledge. An agent framework can coordinate planning and memory. MCP gives these systems a consistent way to exchange context and invoke tools.
Where to begin
My preferred starting point is deliberately small: one host, one server, one workflow, and one outcome that can be measured. Keep a person in control of consequential actions. The first milestone is not an autonomous enterprise platform. It is evidence that one carefully governed capability makes real work faster or more reliable.
Once that boundary is dependable, reuse becomes the multiplier. Other compatible AI applications can discover the same capability, and the server team can improve its contract without rebuilding every client integration. That is how an MCP proof of concept grows into an AI platform strategy.
Official resources
Frequently asked questions
What is Model Context Protocol?
Model Context Protocol is an open standard for connecting AI applications and AI agents to external tools, data sources, and reusable prompts through a consistent interface.
Does MCP replace APIs?
No. MCP commonly sits above existing APIs and data systems, giving AI applications a standard way to discover and use their capabilities.
What is the difference between MCP and RAG?
RAG retrieves relevant information for a model’s context. MCP is a broader interoperability protocol that can expose resources, prompts, and callable tools. A system can use both: RAG for grounded knowledge and MCP for standardized access to context and actions.
Why is MCP important for agentic AI?
Agentic AI needs dependable access to real systems. MCP helps an AI agent discover capabilities, understand schemas, call tools, and receive structured results without a custom integration for every host and server combination.
Who created MCP, and does OpenAI support it?
MCP was created and open-sourced by Anthropic in 2024. OpenAI later became an early adopter and core contributor, uses MCP for connectors and apps in ChatGPT, and supports MCP servers through the OpenAI Agents SDK.